Your entire ISO/IEC 27001 ISMS, tailored to you in minutes
Blueprint by Aegora GRC turns five simple inputs into a complete, tailored set of information security policies, procedures, registers and templates — the full documented ISMS foundation your auditor expects, fully yours to edit.
The complete kit is free with an account — no credit card, no trial limit.
Plus a free 1-hour expert consultation
Free · no credit card · no subscription
- ISO/IEC 27001:2022 · clauses 4–10 + Annex A
- No credit card required
- Instant access after sign-up
- Free — no subscription
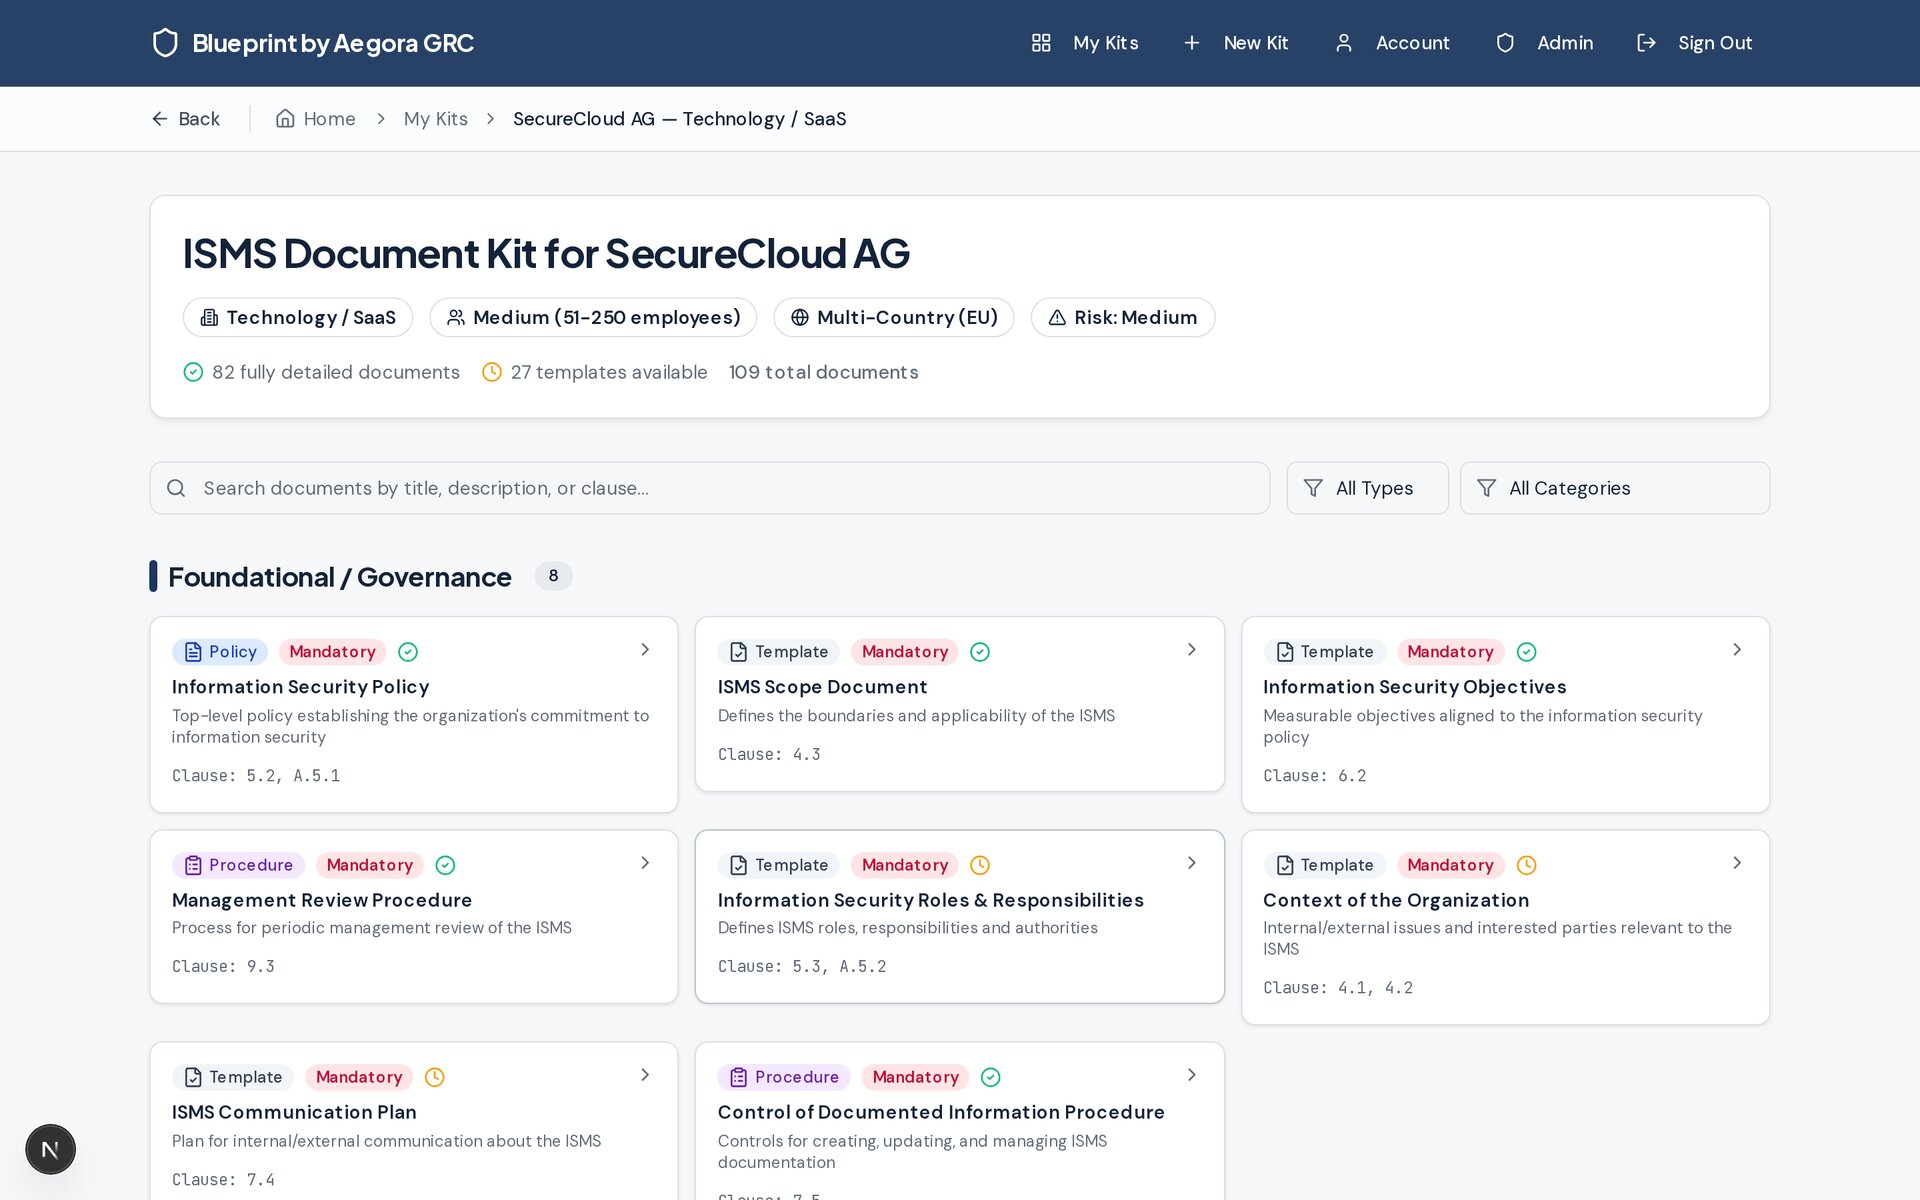
109
ISMS documents
19
Mandatory documents included
93
Annex A controls mapped
Free
For the complete kit
Unblock security reviews this week, not next quarter
Answer security questionnaires fast
Hand enterprise buyers a complete, professional ISMS document set and keep the deal moving.
Skip the $30k+ consulting bill
Consultant-led ISO/IEC 27001 projects in the US commonly run $30,000–50,000. Start from a ready-made, tailored kit instead.
A documented ISMS in an afternoon
Five inputs, a full document set in minutes, editable Word and PDF files you own.
The complete documentation kit is free — you only pay if you want expert consulting.
Regulatory coverage
How ISO/IEC 27001 covers the rules that apply to you
Implementing ISO/IEC 27001 already covers much of what other standards and regulations in your market require. The remaining gaps are where our consultants help.
Frameworks relevant in United States
Covered by your ISO/IEC 27001 documentation
Select a framework to see the breakdown
AICPA Trust Services Criteria (SOC 2)
Mapped to ISO/IEC 27001:2022
- Data Privacy (48%)
- Business Continuity & Disaster Recovery (33%)
- Data Classification & Handling (56%)
- Identification & Authentication (80%)
- Physical & Environmental Security (62%)
- Security, Compliance & Resilience Governance (30%)
- Third-Party Management (83%)
- Human Resources Security (68%)
- Continuous Monitoring (66%)
- Risk Management (54%)
- Network Security (58%)
- Incident Response (68%)
- Asset Management (77%)
- Cryptographic Protections (63%)
- Change Management (47%)
- Information Assurance (41%)
- Compliance (64%)
- Security Awareness & Training (32%)
- Project & Resource Management (69%)
- Technology Development & Acquisition (63%)
- Vulnerability & Patch Management (80%)
- Configuration Management (62%)
- Endpoint Security (33%)
- Threat Management (55%)
- Secure Engineering & Architecture (76%)
- Artificial Intelligence & Autonomous Technologies (0%)
- Capacity & Performance Planning (52%)
- Security Operations (73%)
- Cloud Security (59%)
- Mobile Device Management (53%)
Indicative overlap calculated with the Secure Controls Framework (SCF) 2026.3, assuming all 93 ISO/IEC 27001:2022 Annex A controls are implemented. After sign-in, your dashboard scores your own Statement of Applicability. Not a compliance assessment or legal advice.
Built for the people who own ISO/IEC 27001
Whatever brought you here, you need credible documentation fast — without a six-figure project.
Founders & CTOs
An enterprise prospect just sent a security questionnaire asking for ISO/IEC 27001.
Show a complete, professional ISMS document set this week — not next quarter — and keep the deal moving.
IT & Security Managers
You own the certification project but have no dedicated compliance team or budget for months of consulting.
Start from a coherent, cross-referenced kit with clear editable sections, so you spend time implementing — not writing.
Consultants & vCISOs
Rebuilding the same policies for every client eats into your margin.
Build tailored kits for multiple company profiles and focus your billable hours on advice and audits.
Compliance & Quality Leads
You need to know exactly which documents the standard requires and prove nothing is missing.
Every document is flagged mandatory or optional and mapped to clauses 4–10 and the 93 Annex A controls.
Everything you need for a certifiable ISMS
Purpose-built for ISO/IEC 27001:2022 — not a generic template pack. Every document is coherent, cross-referenced and tailored to your organization.
Complete Document Kit
Receive a full, tailored ISO/IEC 27001:2022 ISMS set — policies, procedures, registers and templates — in one place.
Tailored to Your Business
Five simple scoping inputs adapt every document to your industry, size, geography and risk appetite.
Annex A Aligned
Mapped to the 93 Annex A controls with a customizable Statement of Applicability built in.
Auditor-Ready Documents
Professional document control, versioning and classification on every page — the documented ISMS your auditor reviews at certification.
Minutes, Not Months
Skip the blank page. Produce a coherent, cross-referenced ISMS in an afternoon instead of quarters.
Word & PDF Export
Download fully formatted, editable Word and PDF files you own and can refine to match your organization.
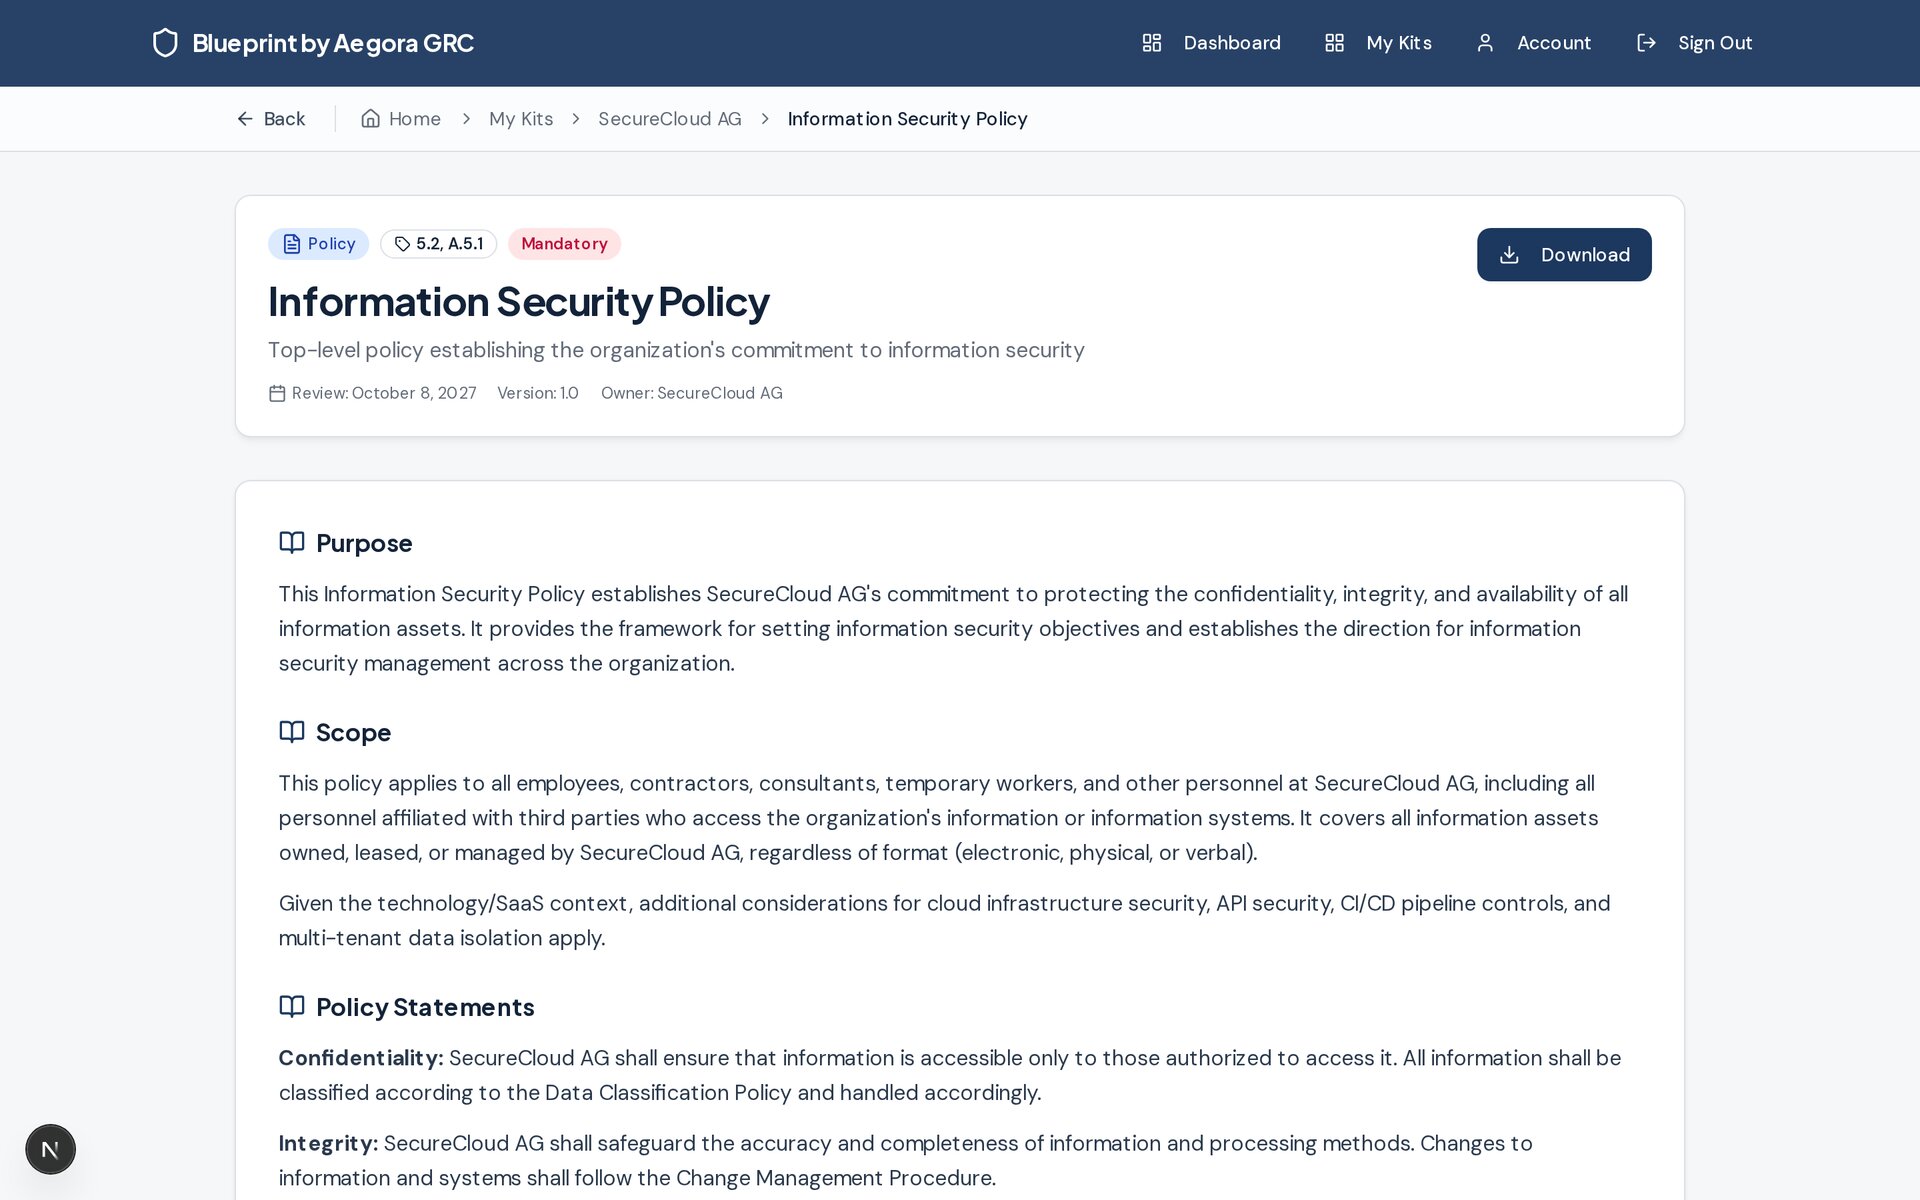
Documents that actually fit your organization
Instead of hunting for templates and stitching them together, get a consistent kit where every policy, procedure and register reflects your real scope.
- Industry, size, geography and risk appetite baked into every document
- Editable callout sections show exactly what to customize
- Consistent document control, versioning and classification
- Customizable Statement of Applicability across all Annex A controls
From zero to a complete documented ISMS in three steps
Describe your organization
Answer five quick questions about your company, industry, size, footprint and risk appetite.
Receive your tailored kit
We assemble a complete, tailored ISMS document set aligned to ISO/IEC 27001:2022 in seconds.
Customize & export
Fine-tune editable sections, then download polished Word and PDF documents ready for your auditor’s review.
Consultant quality, for free
See how a tailored kit compares with the usual ways of getting ISO/IEC 27001 documentation.
| Hiring a consultant | Free templates | Blueprint by Aegora GRC kit | |
|---|---|---|---|
| Cost | Days of billable consulting | Free or cheap | Free |
| Time to a complete draft | Weeks to months | Weeks of stitching together | Minutes |
| Tailored to your scope | |||
| ISO/IEC 27001:2022 clauses 4–10 + Annex A | |||
| Mandatory vs optional clearly flagged | |||
| Editable Word & PDF you own |
Free kit. Expert help when you need it.
The complete documentation kit is free. When you want hands-on help implementing it, our consultants are ready.
Full documentation kit
Everything included — free with an account.
Free
No credit card required
- All 109 documents, incl. the 19 mandatory ones
- Unlimited Word & PDF downloads
- Customizable Statement of Applicability
- Tailored kits for multiple company profiles
- Editable, certification-grade formatting
- No credit card required
- Instant access after sign-up
- Free — no subscription
Expert consulting
Implementation, gap analysis and audit preparation by ISO/IEC 27001 specialists.
Custom scope & pricing
Free 1-hour expert consultation
Book a one-on-one call with an ISO/IEC 27001 specialist to review your kit and plan next steps — free.
- Gap analysis against ISO/IEC 27001 and local regulations
- Implementation support & risk assessment workshops
- Internal audit & certification-audit preparation
- Ongoing vCISO & compliance support
Consulting & Implementation Services
Expert help to implement, operate and certify your ISMS
Guided implementation
Hands-on, step-by-step support to roll out the full ISMS — turning the document kit into a working management system with your team.
Audit services
Internal audits, gap assessments and certification-readiness reviews to confirm your controls hold up before the certification body arrives.
Workshops & training
Tailored workshops and awareness sessions that upskill your staff on ISO 27001:2022, risk management and their security responsibilities.
vCISO services
A virtual CISO to provide ongoing security leadership, manage risk, and keep your ISMS effective and improving over time.
Custom scope & pricing — tell us what you need.
Trusted by security and compliance teams
“We had a defensible ISMS in an afternoon. What used to be a six-month consulting engagement is now a starting point we actually own.”
Lukas Meier
CISO, FinTech scale-up
“The documents are genuinely tailored — not generic boilerplate. Our auditor commented on how coherent and cross-referenced everything was.”
Sabine Keller
Head of IT, Healthcare
“The Statement of Applicability and registers alone saved us weeks. Getting the full kit free made the decision easy.”
Anna Lindqvist
Compliance Lead, SaaS
“Clear document control, versioning and classification on every page. It looks like it came out of a top-tier consultancy.”
Marcus Feld
COO, Managed Services
Frequently asked questions
Straight answers to what people ask us most.
Is this aligned with the current ISO/IEC 27001:2022 standard?
The kit maps to clauses 4–10 and all 93 Annex A controls. It flags 19 core documents for your implementation. ISO/IEC 27001 requires documented information, not a fixed number of separate files; control applicability depends on your risks and obligations.
Will these documents get me certified?
They give you the complete documentation an auditor expects, tailored to your scope. Certification also requires implementing the controls and passing an audit by an accredited certification body — our consulting team can help with that if you need it.
Is it really free?
Yes. Create an account and get every document with unlimited Word and PDF downloads — no credit card, no subscription, no trial limit. We earn from optional consulting services.
What does consulting cost?
Consulting is scoped to your needs — from a single gap analysis to full implementation and audit preparation. Start with a free 1-hour consultation and we will propose a fixed quote.
Can I edit the documents?
Absolutely. Every document exports as an editable Word file (and PDF), with highlighted sections showing exactly what to adapt to your organization.
I am a consultant — can I use it for several clients?
Yes. You can create multiple company profiles and receive a dedicated, tailored kit for each one.
Build your ISO/IEC 27001 ISMS today
Create a free account and get the complete, tailored document set. Need hands-on help? Our consultants are one click away.
Plus a free 1-hour expert consultation
Full kit — free
Plus a free 1-hour expert consultation